Configure Single Sign-On (SSO)
This feature is only available at request. Please contact support@aichat.com for more information to enable this feature.
Single Sign-On (SSO) simplifies user access and strengthens account security by allowing your team to sign in to AiChat through your organization’s centralized Identity Provider (IdP).
Prerequisites
Before configuring SSO, make sure the following requirements are met:
- AiChat administrator access: You must be an Organization Administrator for the organization you want to configure.
- Identity Provider permissions: You must have sufficient administrator permissions in your Identity Provider to create and configure an OIDC or SAML application.
- Populated email fields: AiChat uses email addresses to identify and match user accounts. Each directory user must have a valid email address that matches the email used for their AiChat account.
- SSO feature access: SSO must be enabled for your organization according to your subscription or contract.
Supported Identity Provider
AiChat currently supports the following Identity Providers:
| Provider | Protocol |
|---|---|
| Microsoft Entra ID | OpenID Connect (OIDC) |
| Google Workspace | Security Assertion Markup Language 2.0 (SAML 2.0) |
Admin Setup and Sign-In Controls
As an Organization Administrator, you can add, test, and activate an SSO connection from your organization settings.
Once the SSO feature is enabled, you can control which sign-in methods members of your organization are allowed to use. At least one of the following sign-in methods must remain enabled:
- Magic Link: Authentication using a link sent to the user’s email address. This method is default option.
- SSO: Authentication through the organization’s configured Identity Provider. This method requires the SSO feature to be enabled.
SSO User Exception List
You can add selected users to the SSO exception list. Users on this list are not required to use SSO and can sign in using another authentication method enabled for the organization.
This option may be useful for approved external users, service accounts, or administrators who require an alternative sign-in method.
End-User Login Flow
To access an SSO-enabled organization:
- The user opens the organization-specific AiChat login page.
- The user selects Sign in with SSO.
- AiChat redirects the user to the organization’s configured Identity Provider.
- The user completes authentication with the Identity Provider.
- After successful authentication, the user is redirected to the organization dashboard in AiChat.
Setting up SSO Connection
Microsoft Entra ID can be connected to AiChat using OpenID Connect (OIDC).
Before you begin, open AiChat App and the Microsoft Entra admin center in separate browser tabs. You will need to copy information between the two platforms during the setup.
Information Exchange During Set Up
| Copy from | Information | Paste Into |
|---|---|---|
| AiChat App | Redirect URL | Microsoft Entra ID |
| Microsoft Entra ID | Diectory (tenant) ID | AiChat App |
| Microsoft Entra ID | Client (tenant) ID | AiChat App |
| Microsoft Entra ID | Client Secret Value | AiChat App |
Copy all URLs and identifiers exactly as displayed. Changing a character or removing a trailing slash may cause the connection test to fail.
Step 1: Start the connection in AiChat App
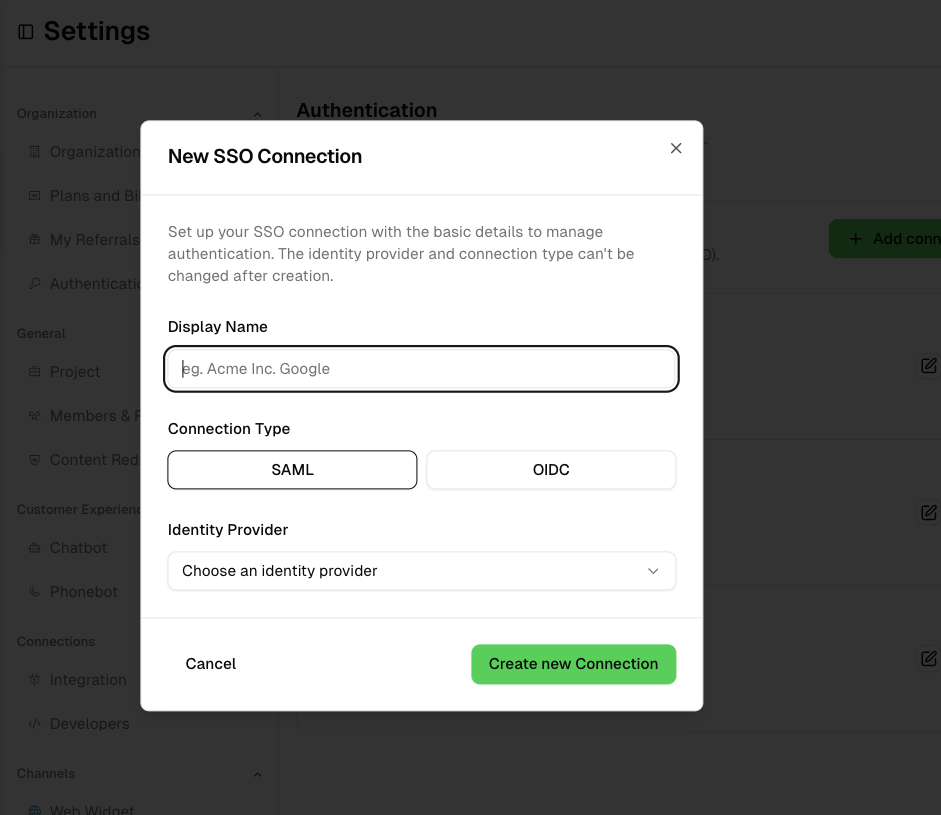
- Sign in to AiChat as an Organization Administrator or Security Manager. Open the organization you want to configure.
- Create a new SSO connection by going to Settings > Authentication > SSO, and click on [+ Add connection]
- In new SSO Connection, input the following
- Display Name: this name will appear on AiChat Login screen when there is more than 1 SSO connection available
- Connection Type and Identify Provider: Select OIDC → Microsoft Entra ID
- Click Create new connection. On the next screen, you’ll be asked to enter more information obtained from Microsoft Entra ID.
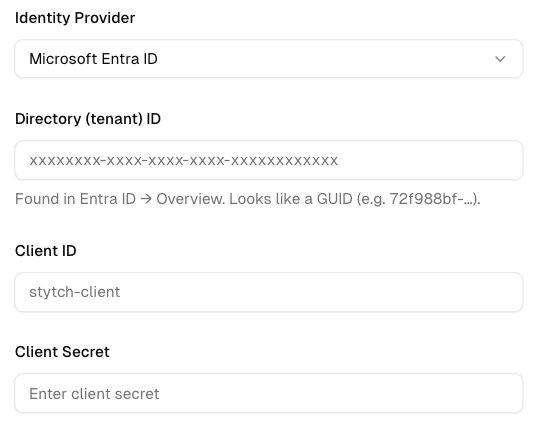
Keep this page open. You will return to it after configuring the application in Microsoft Entra ID
Step 2: Register AiChat in Microsoft Entra ID
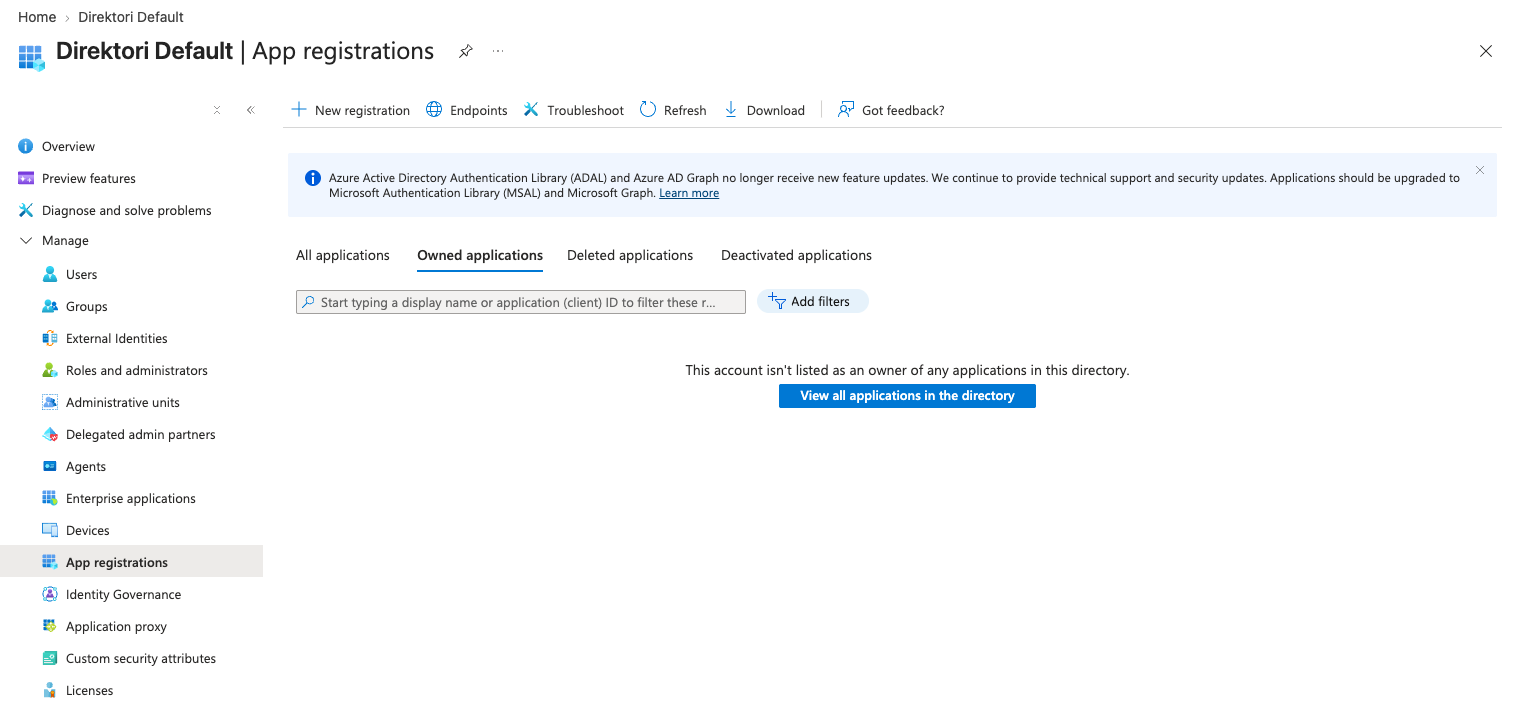
- Sign in to the Microsoft Azure portal, then open Microsoft Entra ID.
- From the left navigation menu, select App registrations, then click + New registration.
- Complete the application details:
- Name: Enter a recognizable name, such as
AiChat – [Organization name]. - Supported account types: Select Single Tenant only, since only your Azure directory will be integrating with AiChat
- Redirect URI: Leave this blank for now. You will configure it in a later step.
- Name: Enter a recognizable name, such as
- Click Register. You will be redirected to the application’s Overview page.
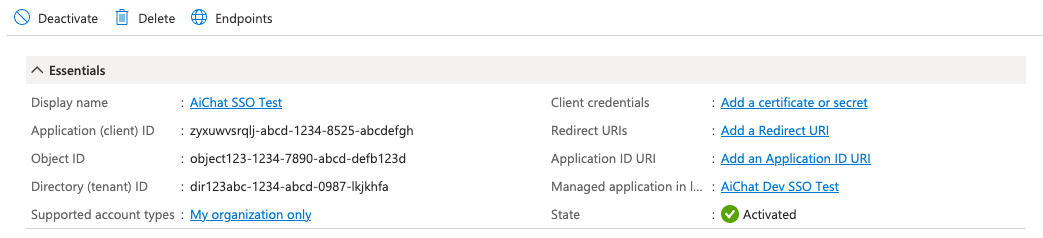
Step 3: Complete the connection in AiChat App.
- From the application’s Overview page in Microsoft Entra ID, copy the following values into the corresponding AiChat fields:
- Copy Directory (tenant) ID into Directory (tenant) ID.
- Copy Application (client) ID into Client ID.
- Create a client secret:
- Under Client credentials, select Add a certificate or secret.
- Select + New client secret.
- Enter a description, choose an expiration period, and click Add.
- Immediately copy the secret from the Value column.
- Paste it into the Client Secret field in AiChat.
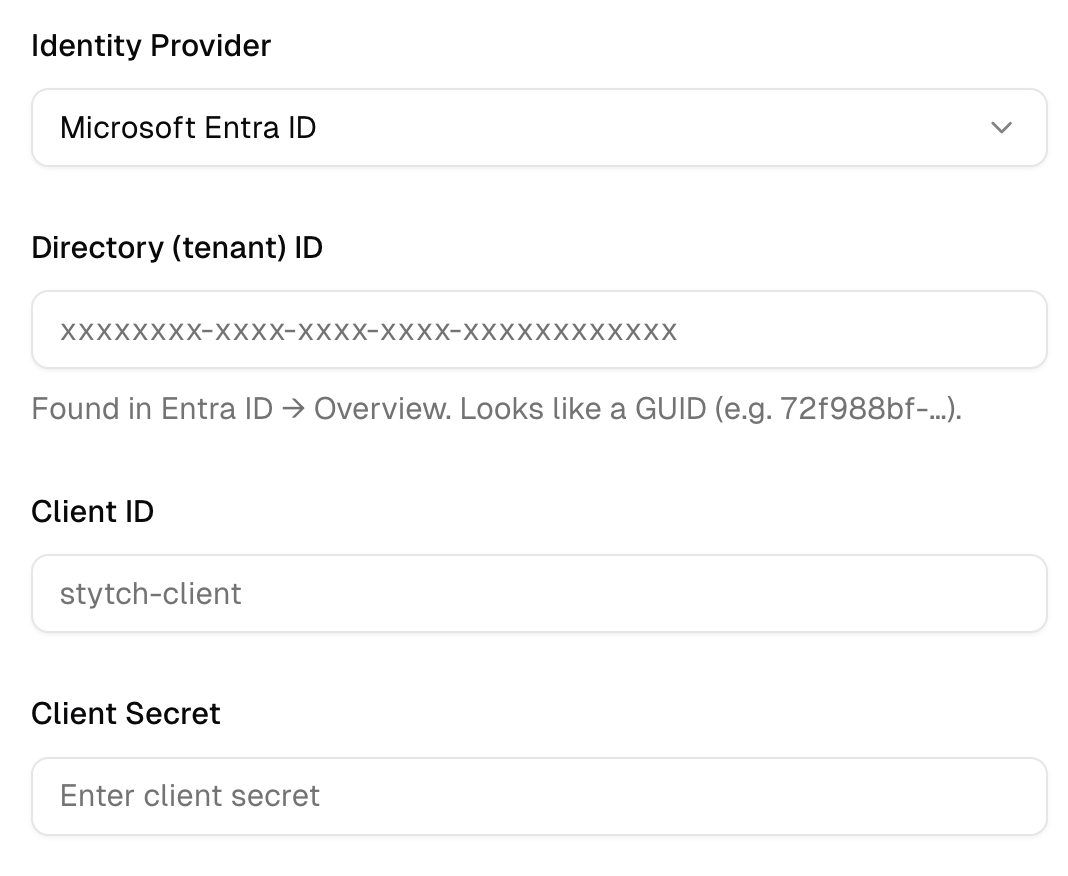
Important: Copy the client secret Value, not the Secret ID. The Value is displayed only once.
- Click Done in AiChat to test the connection.
- If the connection is successful, continue to the next step. If it fails, verify the Tenant ID, Client ID, and Client Secret, then test the connection again.
Step 4: Add AiChat redirect URI to Microsoft Entra ID
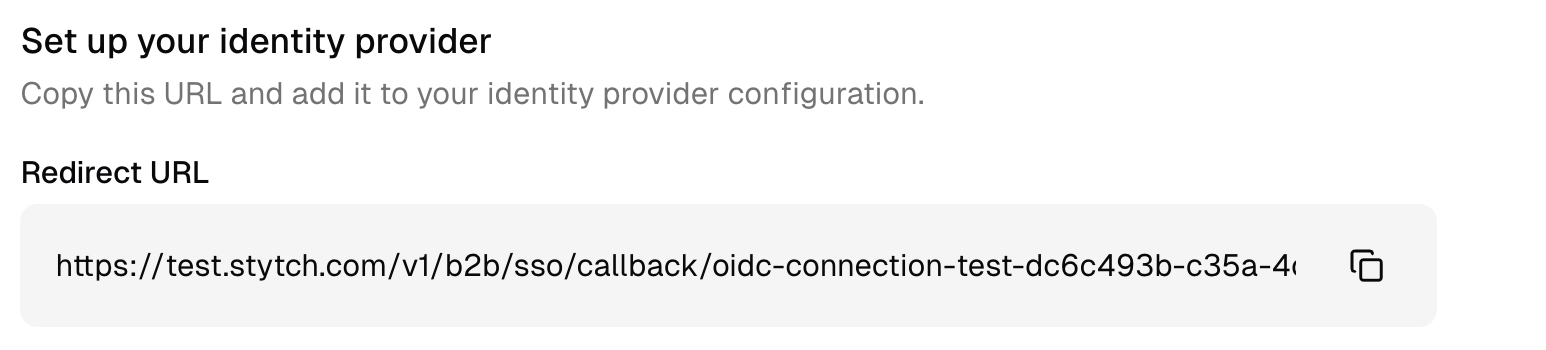
- Copy the Redirect URL from AiChat.
- In Microsoft Entra ID, go to App registrations > [your registered application] > Authentication.
- Under Redirect URI tab, click Add Redirect URI.
- Select Web.
- Paste the AiChat Redirect URL into the Redirect URIs field.
- Click Configure to save the redirect URI.
Step 5: Setup email claims in Azure App Registration
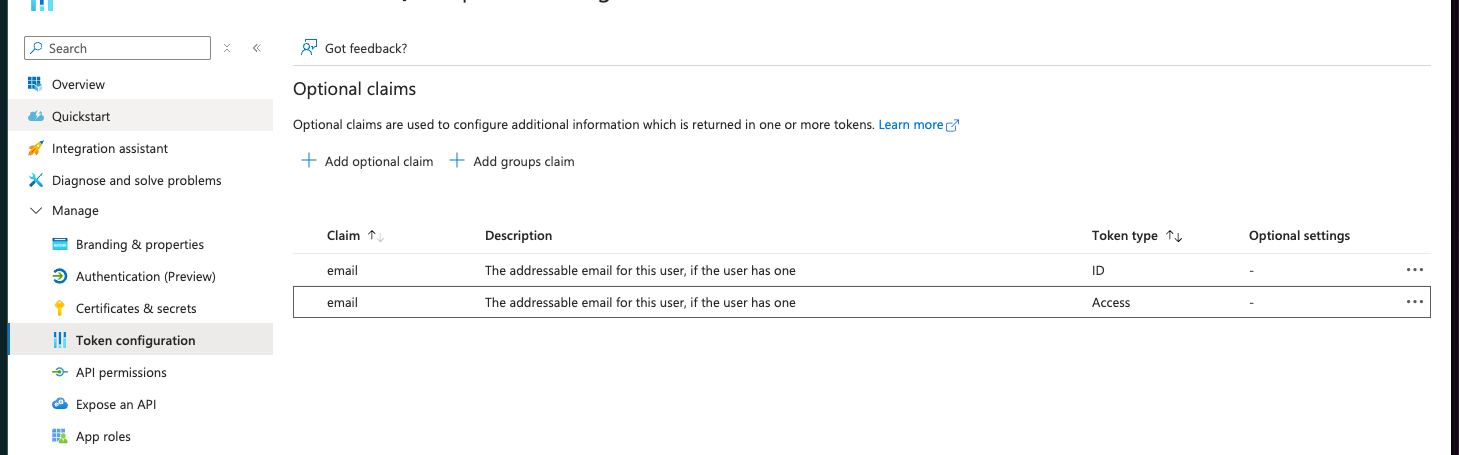
- Under App Registration > Token Configuration, go to + Add optional claim
- Add both ID and Access Token Type with email as claim. You should have 2 email claims in the list
Step 6: Configure API permissions
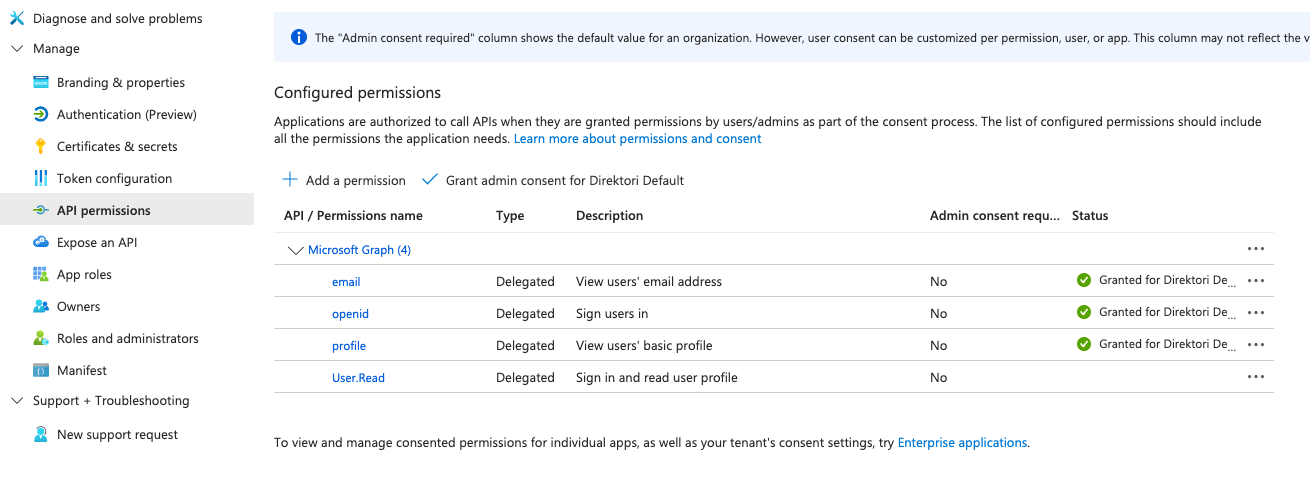
- In Microsoft Entra ID, go to App registrations > [your application] > API permissions.
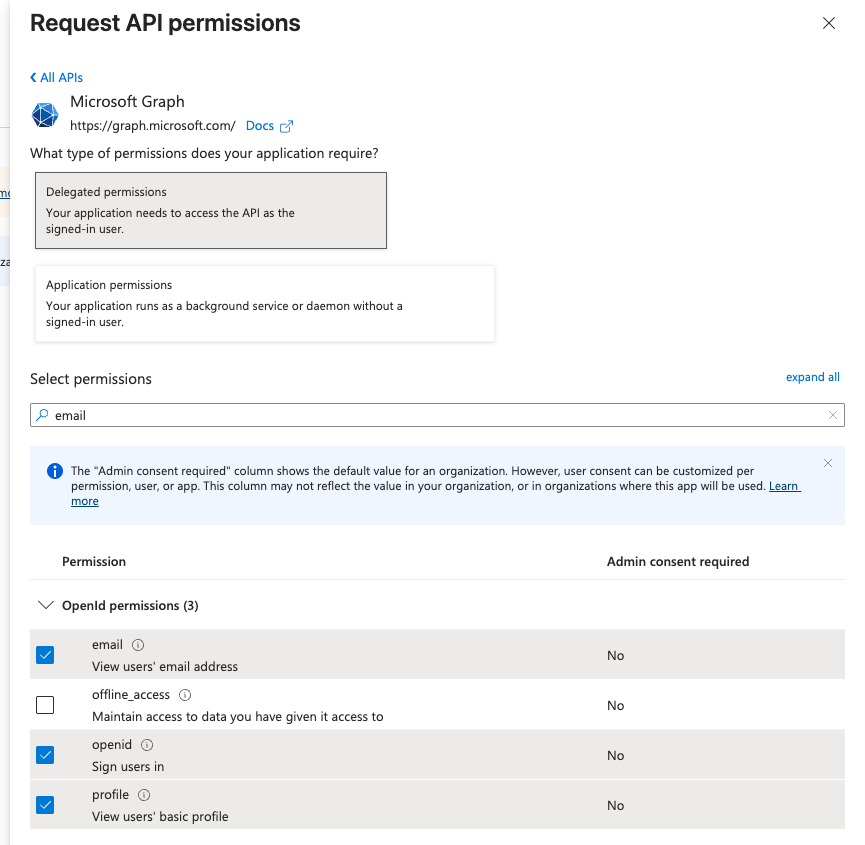
- Click Add a permission, then select Microsoft Graph > Delegated permissions.
- Search for and select these permissions:
emailopenidprofileUser.Read
- Click Add permissions.
- To approve the permissions for all users, click Grant admin consent for [your organization], then confirm by clicking Yes.
Step 7: Add users and test SSO
- Add or invite users to your organization in AiChat platform, then test the SSO connection.
- Ensure each user’s email address in AiChat matches the Email property in Microsoft Entra ID to identify and match the user during SSO authentication.
Ensure each user’s email address in AiChat exactly matches their primary email address in Google Workspace. Enabling access to the Google SAML app does not automatically create an AiChat user account.
Connect using Google Workspace SAML
Before you begin, open the Google Admin console and AiChat Platform in separate browser tabs. You will need to copy configuration details between the two platforms.
Prerequisites
Before starting, ensure that:
- SSO is enabled for your organization in AiChat.
- You have Owner or Organization Administrator access in AiChat.
- You are signed in to Google Workspace as a Super Administrator.
- Each user has a valid primary email address in Google Workspace. AiChat uses this email address to identify and match users.
Information exchanged during setup
| Copy from | Information | Paste into |
|---|---|---|
| Google Workspace | Entity ID | AiChat |
| Google Workspace | SSO URL | AiChat |
| Google Workspace | Certificate | AiChat |
| AiChat | ACS URL | Google Workspace |
| AiChat | Audience URI | Google Workspace |
Copy all URLs, identifiers, and certificate information exactly as displayed. Changing a character, adding spaces, or removing a trailing slash may cause the connection test to fail.
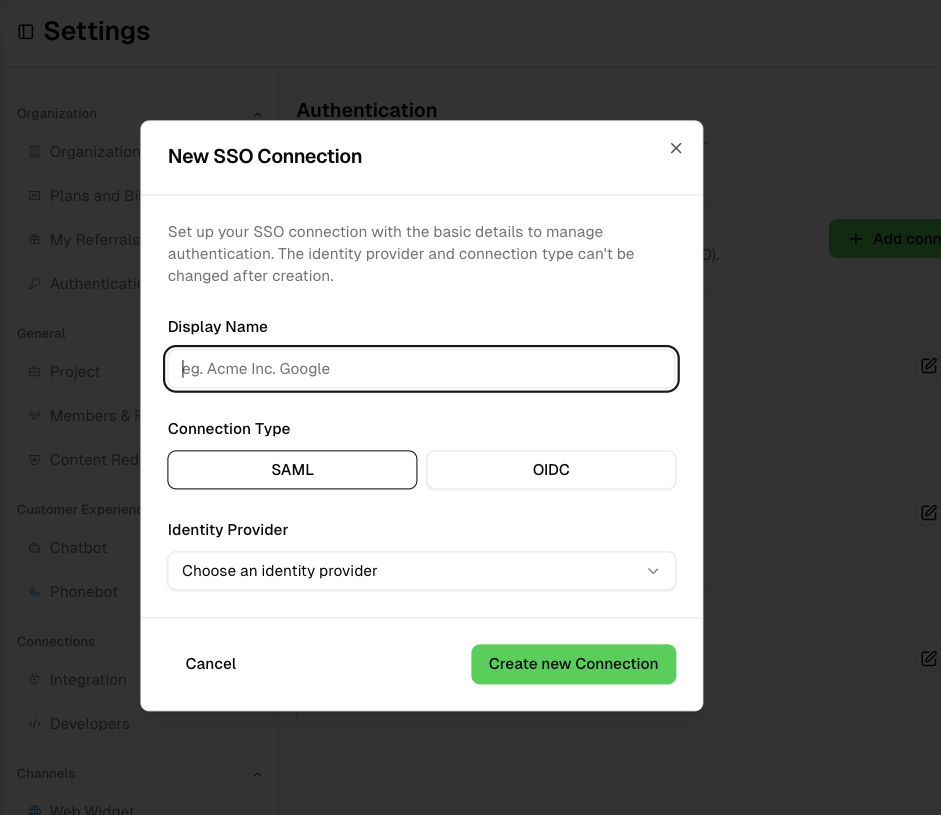
Step 1: Start in AiChat Platform
- Sign in to the AiChat Platform.
- Go to Settings > Authentication > SSO.
- Click + Add connection.
- Complete the following fields:
- Display Name: Enter a recognizable name, such as
Google Workspace. This name appears on the AiChat login screen when more than one SSO connection is available. - Identity Provider: Select Google Workspace.
- Connection Type: Select SAML.
- Display Name: Enter a recognizable name, such as
- Click Create new connection.
- Keep this browser tab open. The next screen contains information you will need when configuring Google Workspace.
Step 2: Create a custom SAML app in Google Workspace
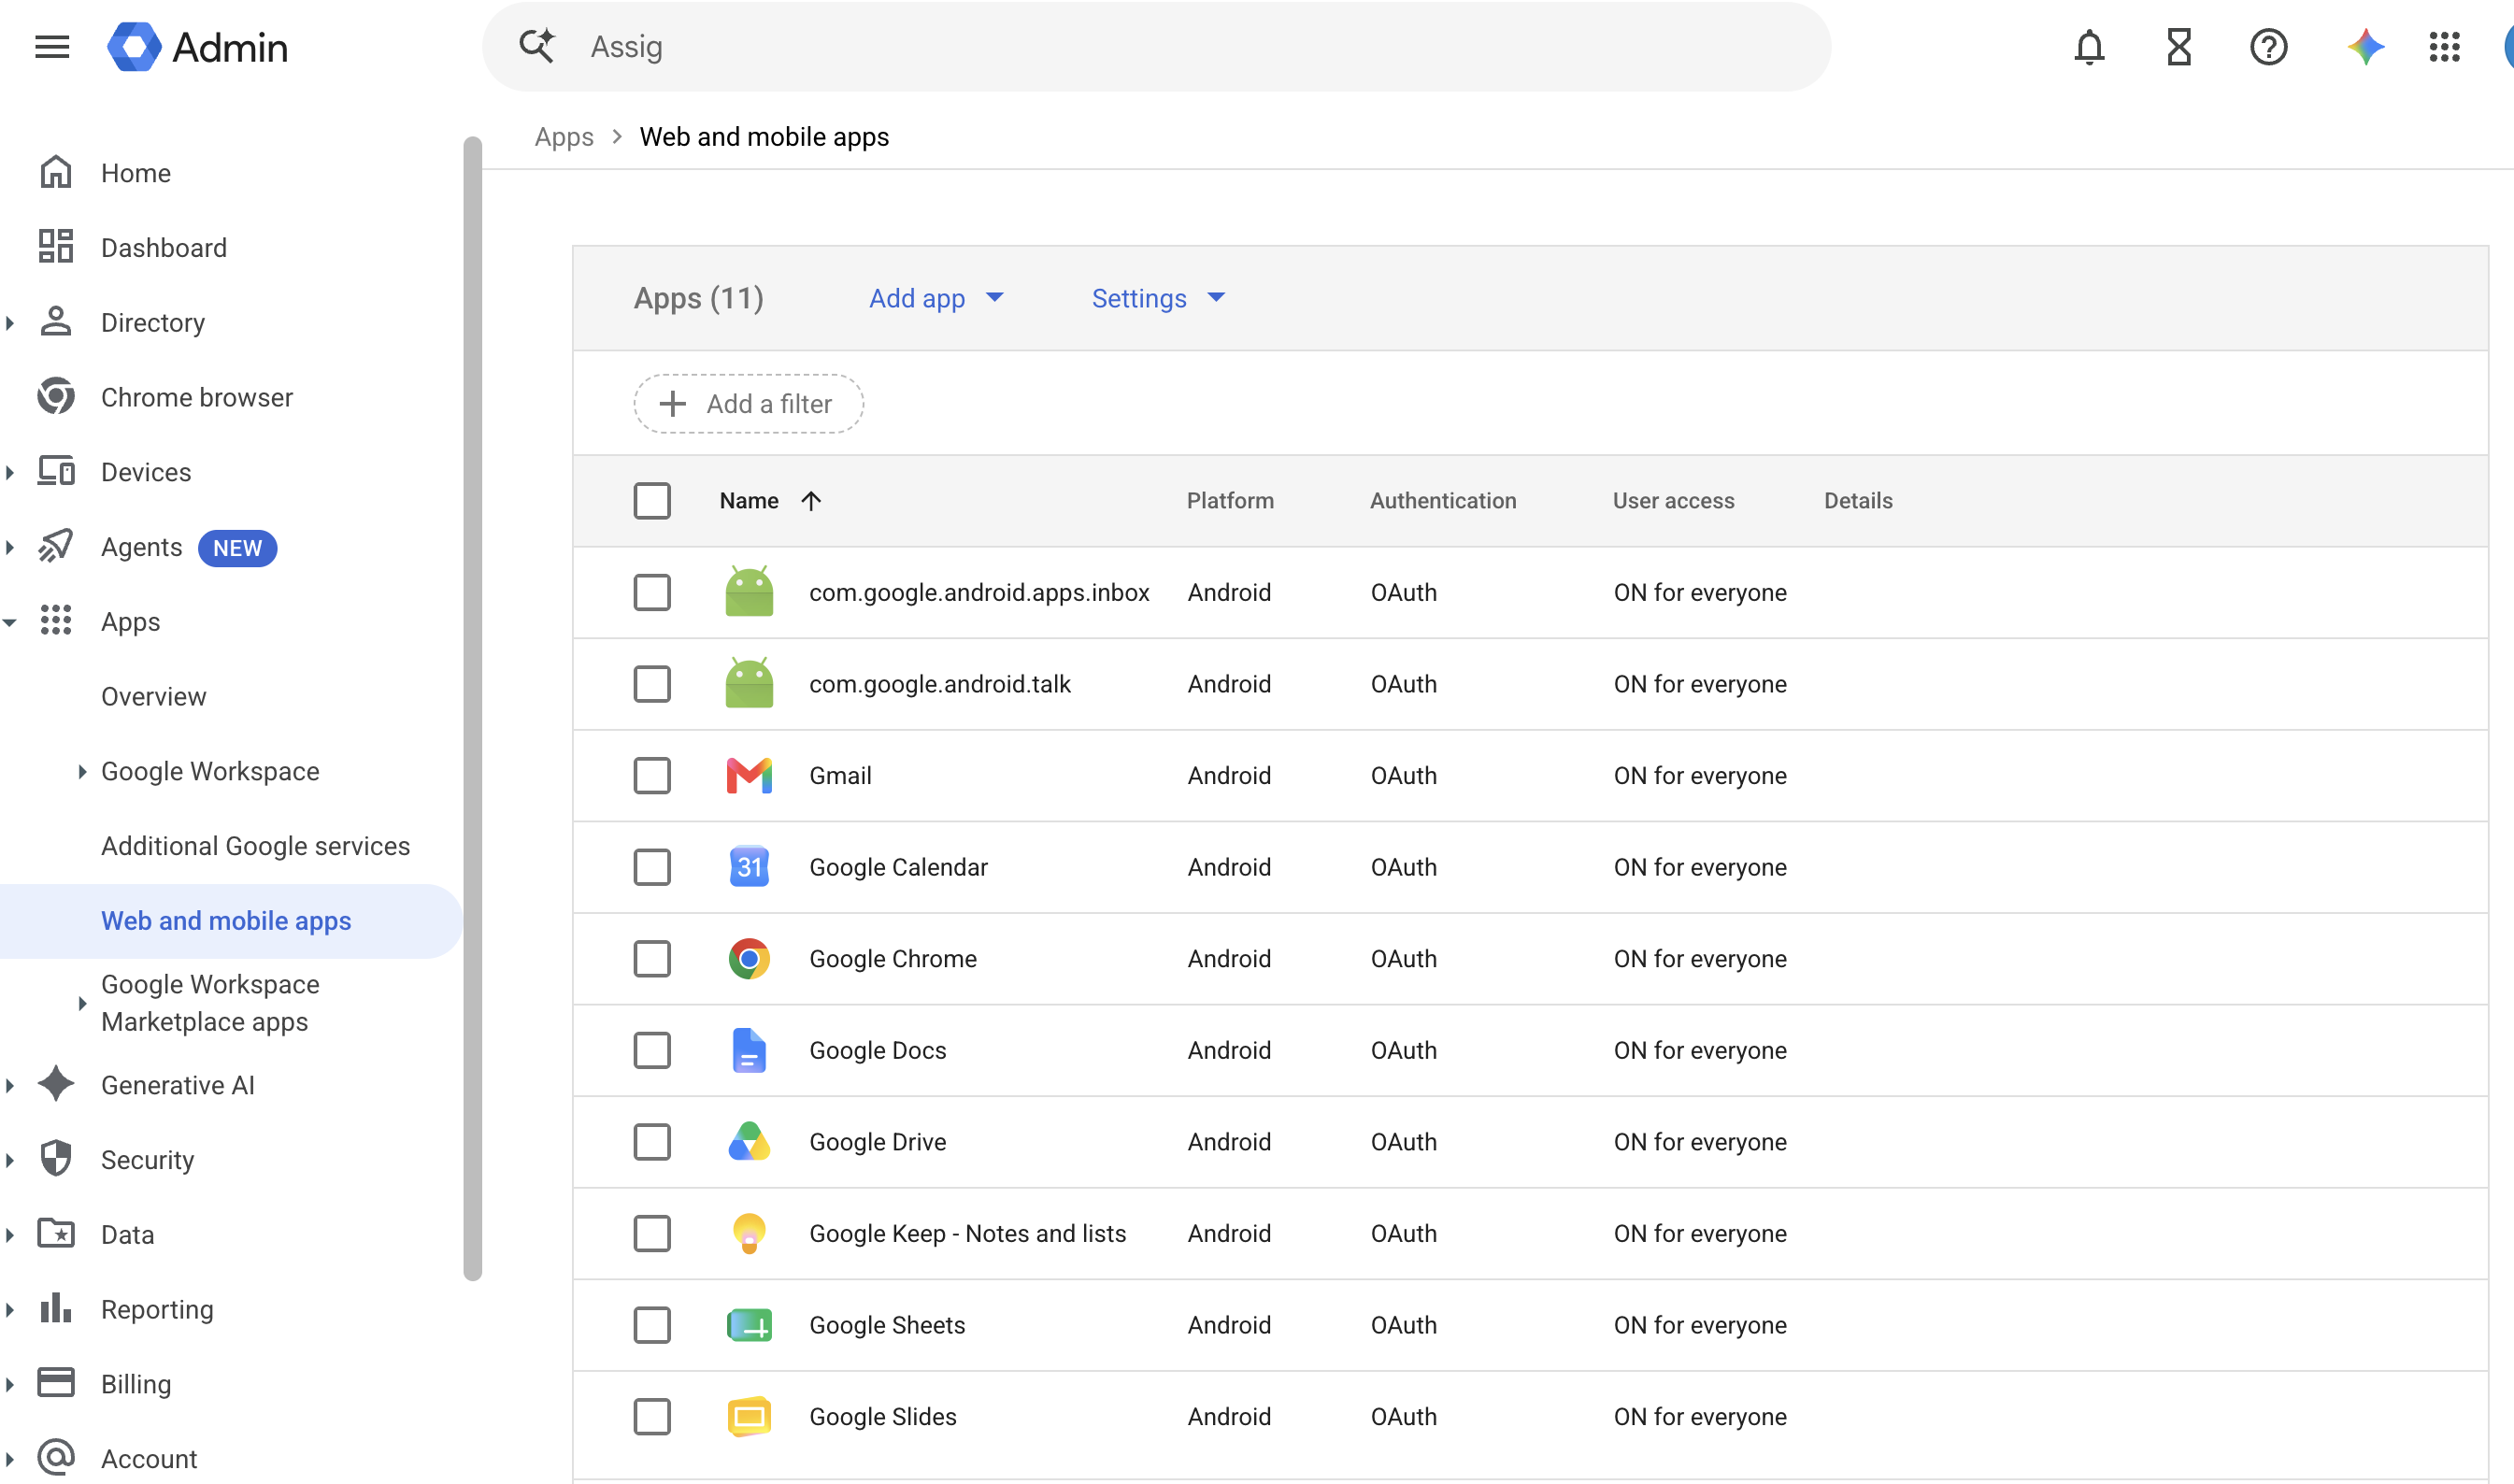
- In a separate browser tab, sign in to the Google Admin console.
- Go to Apps > Web and mobile apps
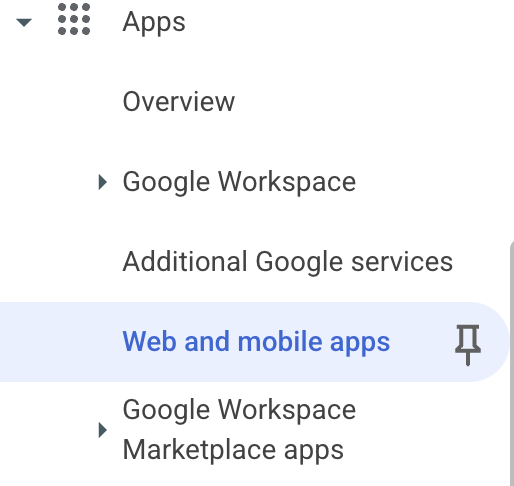
- Click Add app > Add custom SAML app.
- Enter an app name to help you identify it will be integrating with AiChat platform
- Click Continue.
Step 3: Copy Google Workspace information to AiChat
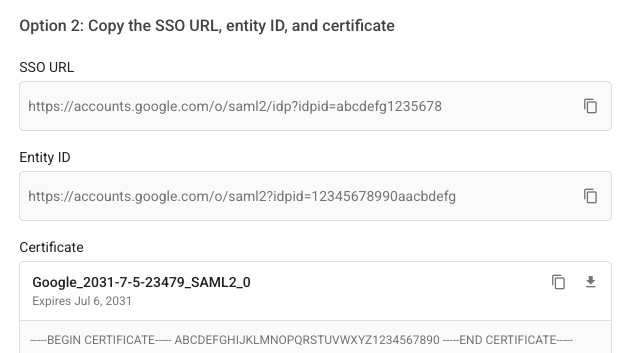
On the Google Identity Provider details page, copy the following information into AiChat:
- Copy Entity ID and paste it into IdP Entity ID.
- Copy SSO URL and paste it into IdP SSO URL.
- Certificate contents → X509 Certificate
Step 4: Add AiChat service provider details to Google
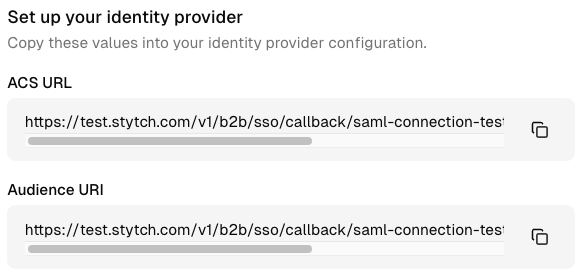
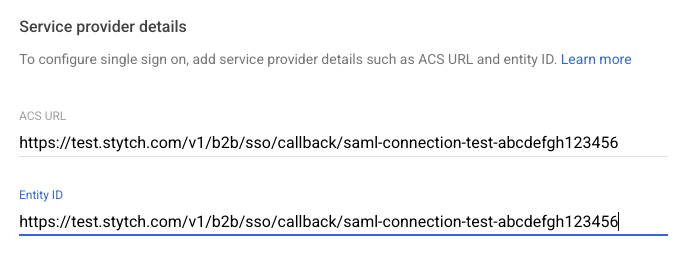
Click next on Google "Add custom SAML app". Copy the following values from AiChat to Google
- ACS URL → ACS URL
- Audience URI → Entity ID
- Under NAME ID, leave ID Format as UNSPECIFIED, and Name ID as Basic Information > Primary Email
- Click Continue.
Step 5: Configure the email attribute
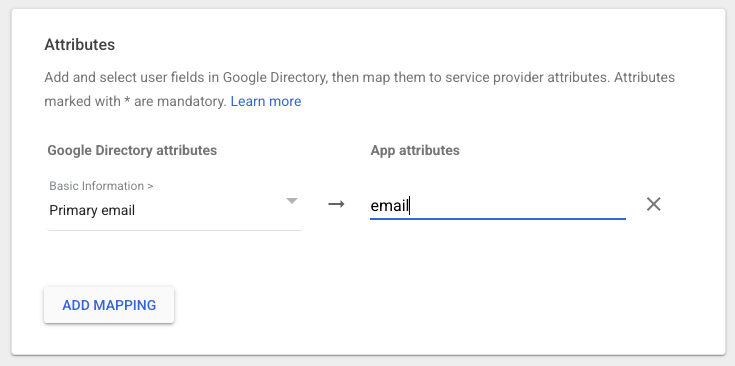
- Under Attribute mapping, click Add mapping.
- Configure the mapping:
- Google Directory attribute: Select Basic Information > Primary email.
- App attribute: Enter
email.
- Click Finish to create the SAML app.
Step 6: Enable user access
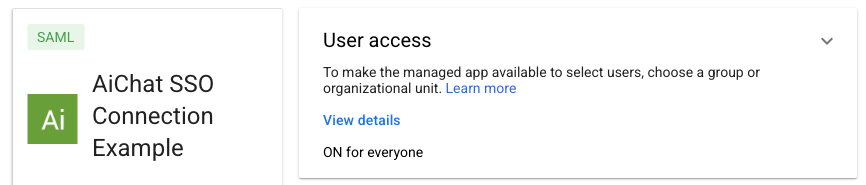
The new SAML app must be enabled before users can sign in.
- Open the newly created AiChat Platform SAML app.
- Click User access.
- Choose who can use the app:
- Select On for everyone to enable access for the entire organization.
- Select specific organizational units or access groups to limit access.
- Click Save.
Google Workspace changes can take up to 24 hours to apply, although they usually take effect sooner.
Step 7: Test and save the connection
- Return to the AiChat Platform.
- Click Test connection.
- Sign in with an authorized Google Workspace account when prompted.
- After the test is successful, save and activate the connection.
Ensure each user’s email address in AiChat exactly matches their primary email address in Google Workspace. Enabling access to the Google SAML app does not automatically create an AiChat user account.
Additional authentication settings
After activating SSO, an Organization Administrator can configure using various login methods that are available. At least one login method must remain enabled.
You can also exclude selected users from mandatory SSO. This allows those users to sign in using another enabled authentication method if your identity provider is temporarily unavailable.
The SSO name can be changed later, subject to availability. SSO names are assigned on a first-come, first-served basis.